If you're building on Lovable and want to make sure what you build is safe for others to use, this one's for you.
As more people ship software with users who rely on it, security becomes part of the product. My team's job is to make sure you never have to handle that on your own, and that you don't need a technical background to get it right.
Here's how it works: what we do and where you come in.
What we handle for you
Much of security on Lovable happens without you ever seeing it. Secure sign-in and access controls are set up by default, secrets are encrypted and never exposed in frontend code, and your app is scanned as you build. That's the same for everyone, including free accounts, because every app should be secure, regardless of what someone pays.
What we flag for you
Every time you publish, our scanners check your code, application logic, database schemas, and row-level security policies, which are the rules that decide who can see and change your data. If something needs attention, we tell you before your app goes live.
Want to go further? Run a deep scan anytime, for free. It takes longer, but it goes deeper. It's built on our own testing system, trained on the security issues that come up most often in Lovable apps.
What we fix for you
Finding problems is only half the job. When the scanner flags something, select Fix. Our agent gets specific instructions for that exact issue and resolves it. The most common issue we see in Lovable apps is data access rules that are too open, and those can be fixed this way in just a few clicks.
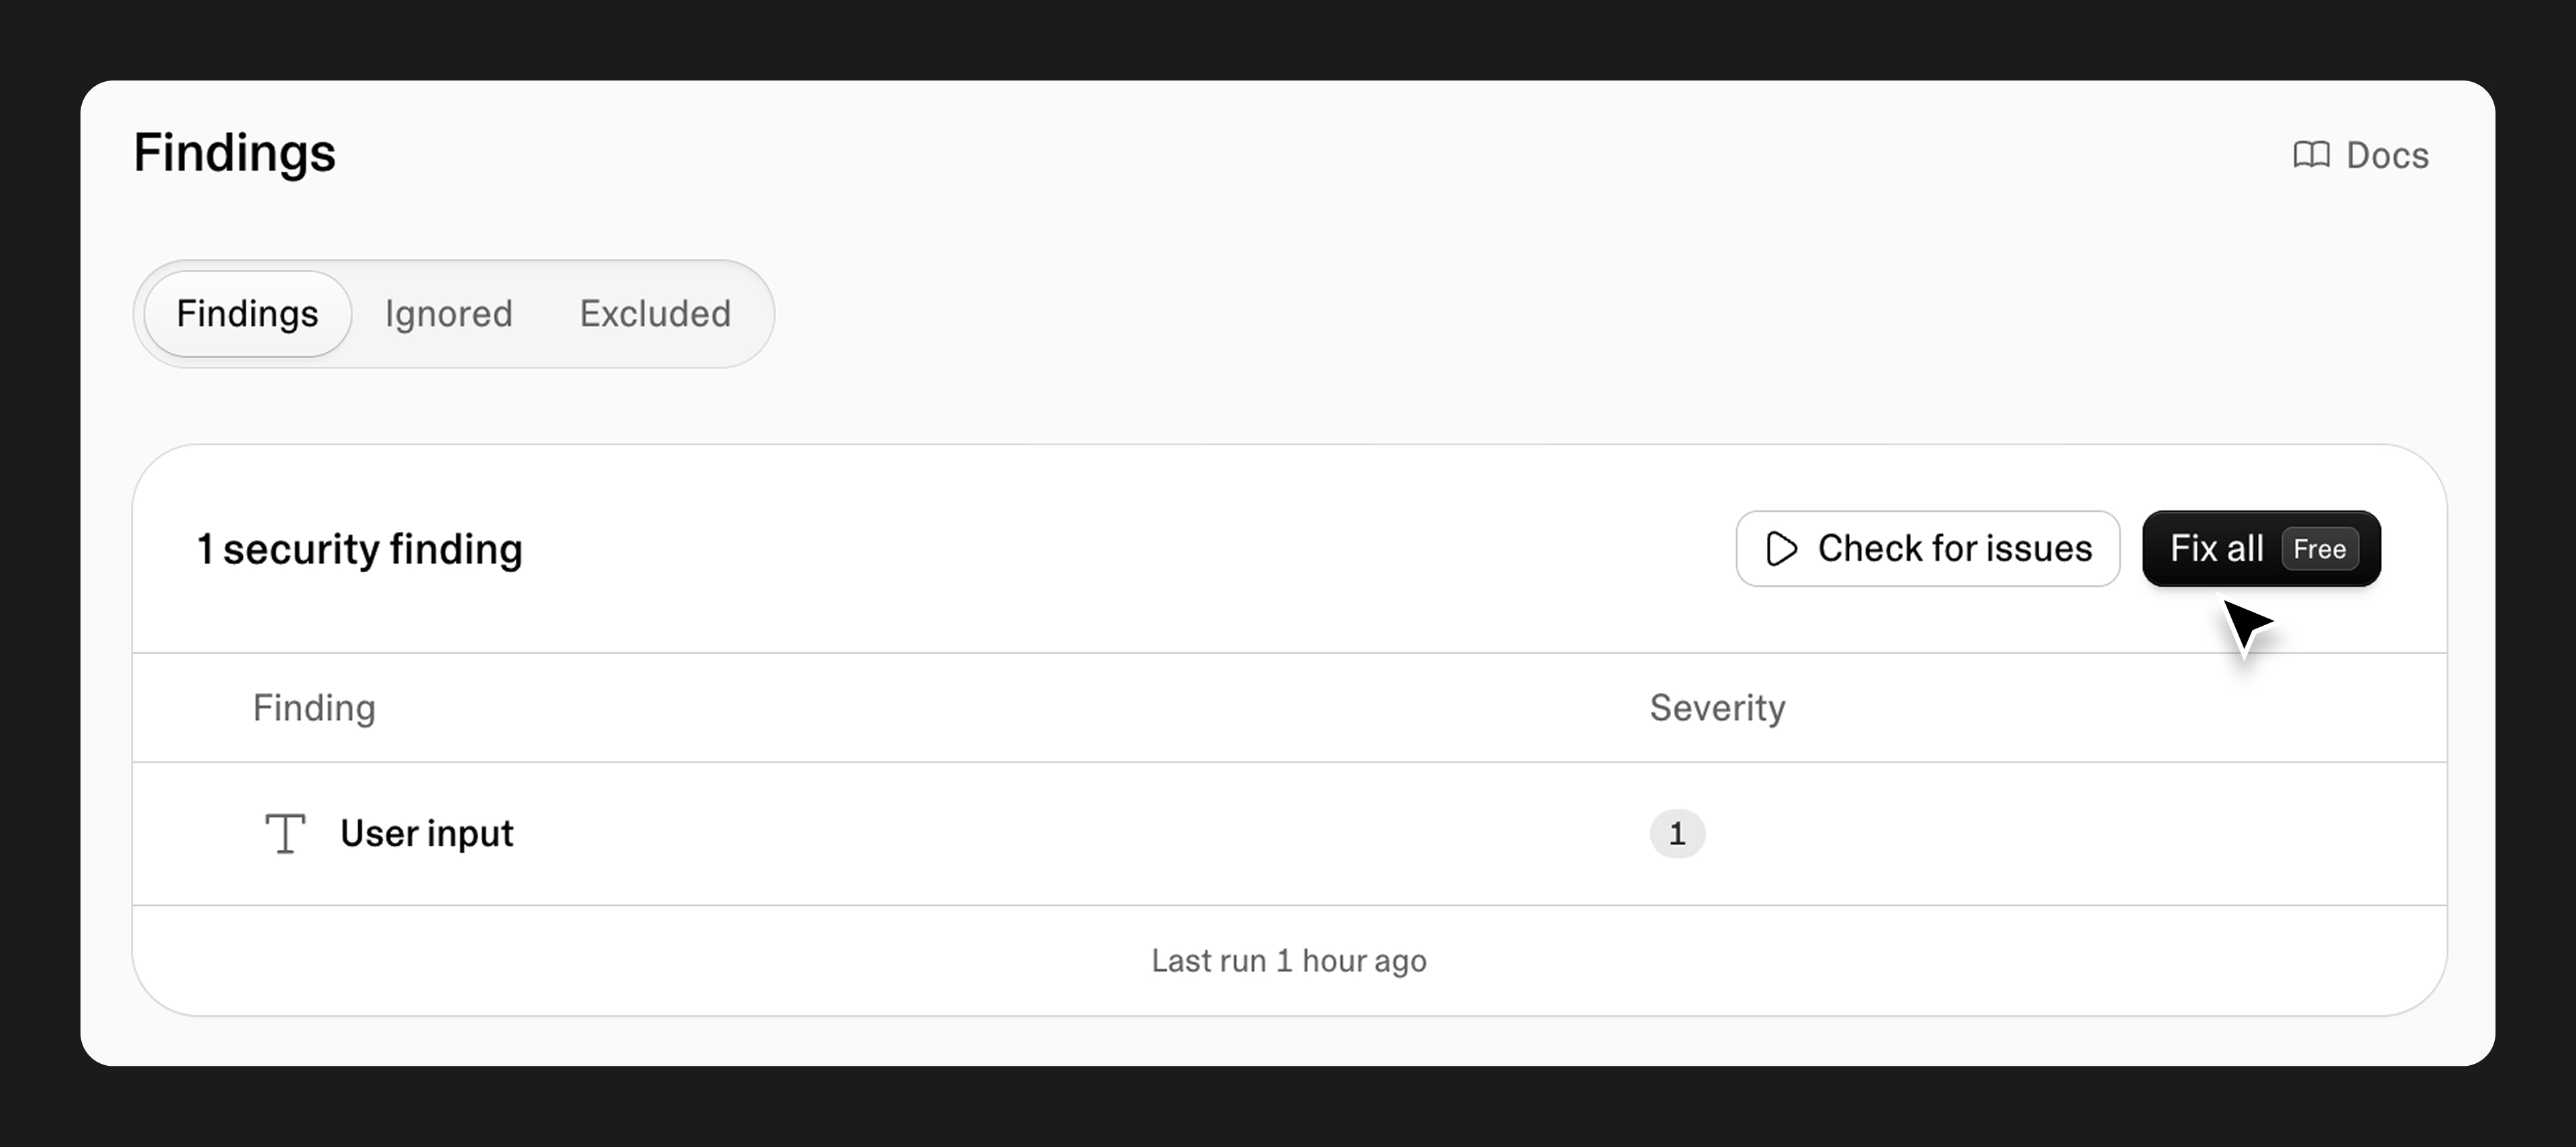
Prefer not to think much about it? Turn on "Auto-fix security issues" in your project settings, and many findings are resolved automatically with your next chat message while you keep building.
We also offer publishing controls that let you, or your workspace admin, if you're on a team, block anything from going live with critical findings.
What we still need you to do
When the scanner flags something, it's important you review the findings and take action, or let auto-fix do it for you. It's the single most effective thing you can do to protect your users.
Sometimes a finding may flag something you've done on purpose, like showing usernames publicly on a forum. You know your app best. We'll do the heavy lifting, but your app is yours, and so is the final call on what goes live.
What's coming this month
- A redesigned security experience: findings that are even easier to read, understand, and act on.
- Scheduled scans on all paid plans: an in-depth scan of your app on a regular schedule, with no extra clicks.
We'll keep carrying as much of the security load as we can, so you can focus on what you're building. In the meantime, start by making a habit of acting on scanner findings, and follow our best practices.
Let's build amazing, secure things together.
— Igor