Your teams already build with Lovable. Now they want to build more advanced apps that use sensitive data in production, and your security team has stricter requirements. Where does the app run, and where does its data live?
Until now, the answer was Lovable's infrastructure. That works for most teams. Some apps, though, rely on data that has to stay inside your network, and some security teams require every production workload to run in an account they own.
Today we're announcing Deploy on AWS, in private preview. Enterprise teams can now run those apps in their own AWS account. Your teams keep building in Lovable the same way they do today.
What runs in your AWS account
Everything an app needs to run lives in a dedicated VPC in your account:
- The Lovable data plane on an Amazon EKS cluster, including the preview sandboxes where builds run while your team iterates
- Published apps, with static assets in Amazon S3 and dynamic requests handled by AWS Lambda
- The app database on Amazon Aurora PostgreSQL, plus app storage in Amazon S3
- Application logs, which can be sent to your own systems, like Amazon S3 or Amazon CloudWatch
- The connector gateway and the secrets for your integrations
Apps reach internal systems, like your data warehouse or CRM, over VPC peering, so those systems stay off the public internet. Lovable installs, manages, and updates everything it deploys there, so your team doesn't take on running it.
Why this matters for teams building on sensitive data
Imagine your HR team wants an app for leave planning. It needs data from your HR system, and your policy says that data can't leave your environment. If the app runs in someone else's cloud, it won't pass that review.
With the workspace in your own AWS account, the app and its data stay there, and the HR system is reached over your private network.
What stays with Lovable
The work of building stays in Lovable's multi-tenant service: the editor, the agent, chat and project history, and workspace settings, identity, and billing.
AI model requests made while building are still processed by Lovable's AI service.
How it works
Hosting on Lovable stays the default, and it's the right fit for most apps. Many organizations will run both, with one workspace in their own AWS account for sensitive data and the rest hosted on Lovable.
To set one up, an admin creates a new Enterprise workspace and chooses to host it in AWS. Lovable generates a CloudFormation stack for your account, and your team reviews it and runs it. The stack creates the VPC, an EC2 instance for the Lovable runner, and the permissions the runner needs. The runner then sets up the EKS cluster, Aurora PostgreSQL, S3, and the other services it needs.
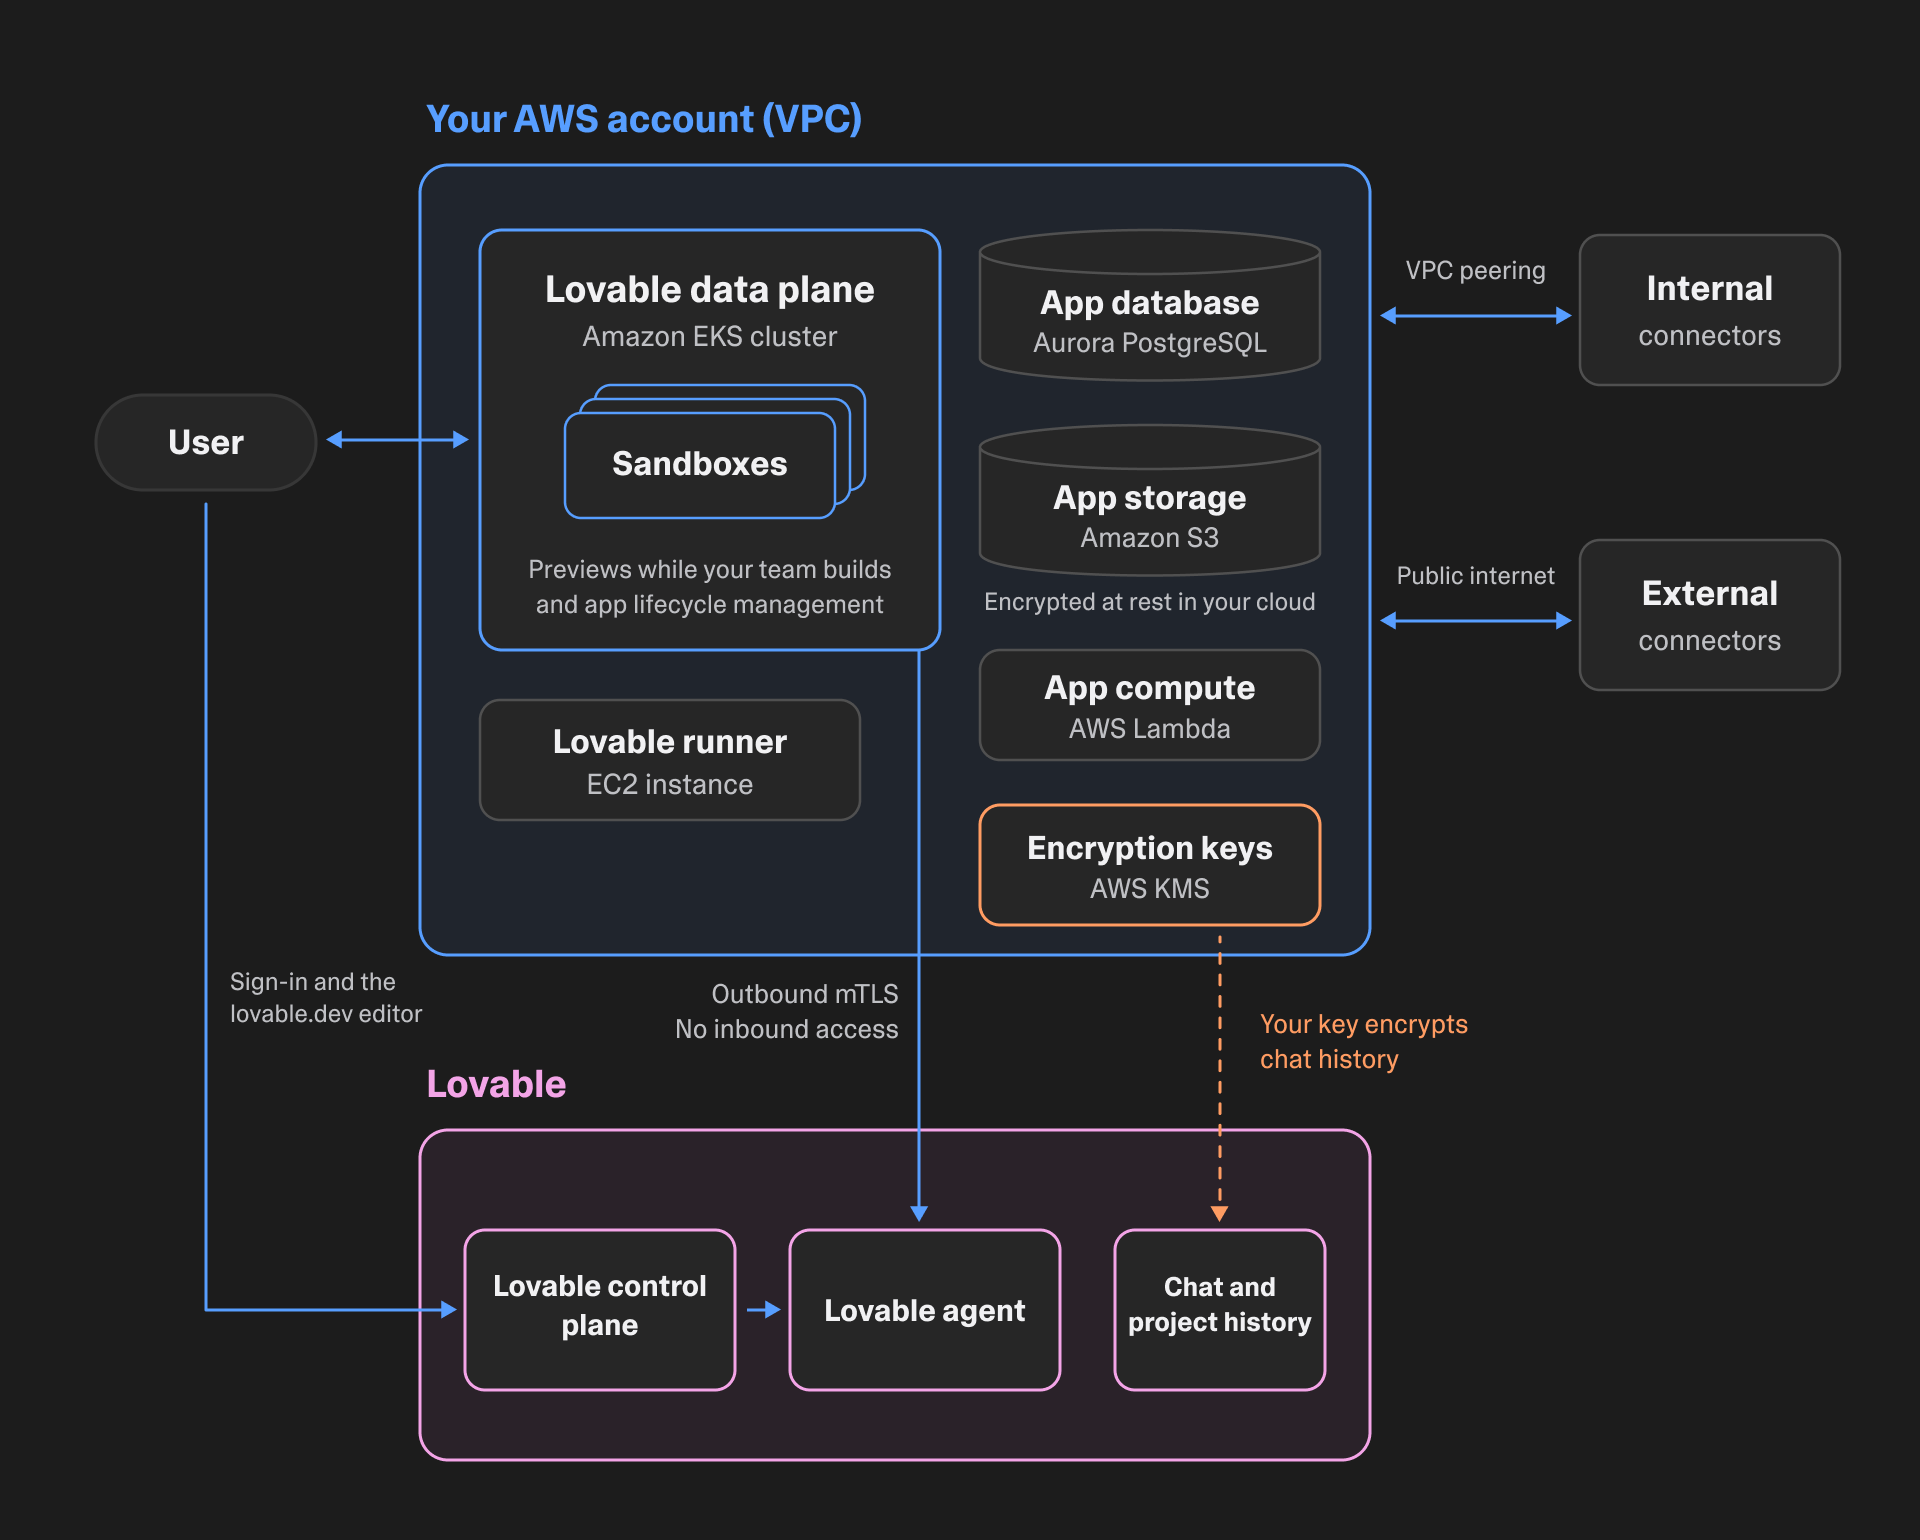
The runner is how Lovable manages your installation while you keep visibility into everything it does. It uses separate IAM roles for setup, day-to-day maintenance, and decommissioning, so it follows the principle of least privilege the whole time, and Lovable's runner endpoint is the only external host it talks to. Each update to the components in your account is a versioned Helm chart that points to signed container images in your container registry.
Your Enterprise security controls apply here too, including SSO and SCIM, publishing limited to workspace members by default, a security scan on every build, and audit logs.
How your data is protected
- In your account. App data stays in your VPC, under your own AWS encryption and access controls.
- Between your account and Lovable. The components in your account connect out to Lovable over an mTLS-encrypted tunnel. Lovable never needs an inbound connection into your network.
- With Lovable. Chat and project history are encrypted at rest. With bring your own key, admins connect their own AWS KMS key in Workspace settings and can revoke Lovable's access at any time.
Deutsche Telekom went live in October, with its Lovable apps running in its own AWS account.
Our teams, including leadership, love building with Lovable. We have already created thousands of applications and prototypes, but our most sensitive workloads require apps and data to stay strictly within our own network. Running Lovable in our own infrastructure through AskT, our internal AI productivity platform, gives our employees the freedom to build tools connected to internal data while our security team maintains full oversight. We are currently working with our Global HR team to explore and build platforms for employees across the company, and we are proud to be the first global enterprise to deploy Lovable this way. There is high excitement across the organization about being able to use Lovable more broadly with this enterprise-friendly deployment.
The best builders move from idea to production without friction. Through deploying Lovable apps on AWS, customers can now take an idea from Lovable to production inside their own AWS environment — keeping their data, security controls, and governance exactly where they are, and scaling globally on the infrastructure they already trust. We're excited to see the new workloads this unlocks.
Getting started
Deploy on AWS is available in private preview for select Enterprise customers. Some features you get when you host on Lovable aren't available yet, and we're working toward full feature parity. Start with the apps you'd want to build and what your policies require for where they run. Your account team can walk your IT and security teams through the architecture.
To join, talk to your account team or email byoc@lovable.dev. New to Lovable Enterprise? Talk to our sales team.